CISA KEV

ColibriSec Weekend Security Roundup October 26 2026 - Black October Matrix

News

Security Roundup: Collabora & VeloCloud KEV Deadlines, PHP2Shell & HTTP2Shell Aftermath, LiteLLM Supply-Chain RAT, GlobalProtect Ransomware & OpenAI Training Pause (Weekend Edition - October 26, 2026)

Executive Summary: The weekend of October 24–26, 2026, marks the apex of what cybersecurity executives, federal agencies, and threat researchers have universally christened "Black October"—a historic convergence of AI-discovered core language runtime vulnerabilities, rapid-fire CISA Known Exploited Vulnerabilities (KEV) mandates, software supply-chain backdoors, and autonomous machine-speed
By James Luther
CVE-2026-110447 Collabora Online Nextcloud RCE and CVE-2026-114625 Arista VeloCloud SQLi CISA KEV

News

CISA KEV Emergency Directives: Collabora Online Nextcloud RCE (CVE-2026-110447) & Arista VeloCloud SD-WAN SQLi (CVE-2026-114625)

📌Security Roundup Series: Weekend of October 26, 2026 • 7 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-110447 & CVE-2026-114625 (CWE-78 (OS Command Injection) & CWE-89 (SQL Injection)) Severity: CRITICAL (CISA KEV BOD 26-04) (CVSS 9.2 & 9.9) Threat Actor: In-the-Wild Opportunistic & Espionage Intrusion Clusters Status: Actively

By James Luther
Plex2Shell KEV Chain Siemens Romulus CVE-2026-110936 FortiSIEM CVE-2026-106173 and Cisco Expressway

News

Enterprise & KEV Exploit Chains: Plex2Shell RCE, Siemens "Romulus" DLL Sideloading (CVE-2026-110936), FortiSIEM gRPC & Cisco Expressway

📌Security Roundup Series: Weekend of October 26, 2026 • 7 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-96652..96656, CVE-2026-110936, CVE-2026-106173 & CVE-2026-76466 (CWE-918 (SSRF), CWE-427 (Uncontrolled Search Path), CWE-22 (Path Traversal) & CWE-295 (Cert Validation)) Severity: CRITICAL (CISA KEV & ENTERPRISE CORE) (CVSS 7.8 – 10.0) Threat Actor:

By James Luther
ColibriSec Resumen de Seguridad Fin de Semana 26 de Octubre de 2026 - Matriz Black October

Noticias

Resumen de Seguridad: Plazos KEV para Collabora y VeloCloud, Crisis PHP2Shell y HTTP2Shell, Backdoor en LiteLLM, Ransomware en GlobalProtect y Pausa de Entrenamiento en OpenAI (Edición Fin de Semana - 26 de Octubre de 2026)

Resumen Ejecutivo: El fin de semana del 24 al 26 de octubre de 2026 marca el punto álgido de lo que ejecutivos de ciberseguridad, agencias federales e investigadores han bautizado universalmente como el "Black October" (Octubre Negro): una convergencia histórica de vulnerabilidades críticas en lenguajes de programación descubiertas

By James Luther
Cadena KEV Plex2Shell Siemens Romulus CVE-2026-110936 FortiSIEM CVE-2026-106173 y Cisco Expressway

Noticias

Cadenas de Exploits Empresariales y KEV: RCE en Plex2Shell, DLL Sideloading "Romulus" en Siemens (CVE-2026-110936), FortiSIEM gRPC y Cisco Expressway

📌Security Roundup Series: Fin de Semana del 26 de Octubre de 2026 • 7 min de lectura deep dive🛡️Vulnerability Intelligence: CVE ID: CVE-2026-96652..96656, CVE-2026-110936, CVE-2026-106173 y CVE-2026-76466 (CWE-918 (SSRF), CWE-427 (Ruta de Búsqueda No Controlada), CWE-22 (Path Traversal) y CWE-295 (Validación TLS)) Severity: CRÍTICA (CISA KEV E INFRAESTRUCTURA EMPRESARIAL)

By James Luther
ColibriSec Weekend Security Roundup October 19 2026

News

Security Roundup: BeyondTrust Zero-Day, ConnectWise M365 Supply-Chain Breach, Fortinet PEERSTITCH & SiteGuard WAF RCE (Weekend Edition - October 19, 2026)

Executive Summary: The weekend of October 16–19, 2026, confronted enterprise defenders with a relentless wave of nation-state appliance zero-days, cloud identity supply-chain compromises, memory-resident firewall implants, and emerging AI-targeted infrastructure heists. Leading the emergency alerts, CISA, Mandiant, and Google Threat Intelligence Group (GTIG) disclosed active zero-day exploitation of CVE-2026-102764

By James Luther
CVE-2026-102764 BeyondTrust Remote Support Zero-Day Armory Castle SAWFLY BARECLAW

News

CVE-2026-102764: BeyondTrust Remote Support Zero-Day Exploited by Armory Castle to Deploy SAWFLY & BARECLAW

📌Security Roundup Series: Weekend of October 19, 2026 • 6 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-102764 (CWE-346 / CWE-290 (Origin Validation Error / Authentication Bypass by Spoofing)) Severity: CRITICAL (CVSS 9.3) Threat Actor: Armory Castle (UNC5221 / Warp Panda - China-Nexus Espionage) Status: Actively Exploited Zero-Day since Aug 29, 2026;

By James Luther
CVE-2025-61624 Fortinet Auto-Script Path Traversal PEERSTITCH Memory Resident Malware

News

CVE-2025-61624: Fortinet Auto-Script Path Traversal Added to CISA KEV Following PEERSTITCH Memory-Resident Malware Attacks

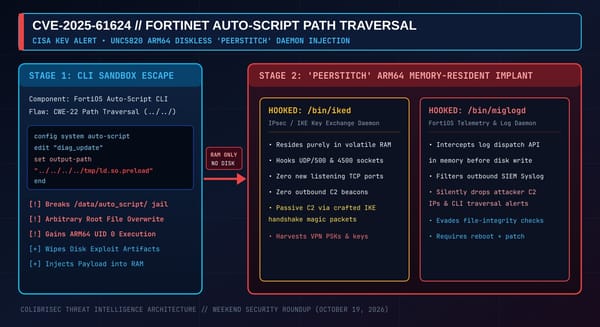
📌Security Roundup Series: Weekend of October 19, 2026 • 6 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2025-61624 (CWE-22 (Improper Limitation of a Pathname to a Restricted Directory)) Severity: HIGH / CRITICAL IN CHAIN (CVSS 5.4 (Chained for Root RCE)) Threat Actor: CL-STA-0954 / UNC5820 (Deploying PEERSTITCH ARM64 Implant) Status: Actively

By James Luther
CVE-2026-0322 Palo Alto Networks PAN-OS Management RCE and Drupal Critical Vulnerabilities

News

CVE-2026-0322 PAN-OS Management Interface RCE & Drupal Critical Advisories (CVE-2026-108097 / CVE-2026-108099)

📌Security Roundup Series: Weekend of October 19, 2026 • 6 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-0322 & CVE-2026-108097 / CVE-2026-108099 (CWE-94 (Code Injection in PAN-OS) & CWE-502 / CWE-94 (Drupal Render Callback Injection)) Severity: HIGH / CRITICAL (CVSS 8.6 (PAN-OS) / 9.8 (Drupal RCEs)) Status: CVE-2026-0322 Exploited in Targeted Attacks

By James Luther
ColibriSec Resumen de Seguridad Fin de Semana 19 de Octubre de 2026

Noticias

Resumen de Seguridad: Zero-Day en BeyondTrust, Brecha M365 en ConnectWise, Malware PEERSTITCH en Fortinet y RCE en SiteGuard WAF (Edición Fin de Semana - 19 de Octubre de 2026)

Resumen Ejecutivo: El fin de semana del 16 al 19 de octubre de 2026 enfrentó a los equipos de defensa corporativa con una intensa oleada de vulnerabilidades de día cero explotadas por actores estatales, compromisos en la cadena de suministro de identidades en la nube, implantes residentes en memoria en

By James Luther
CVE-2026-102764 BeyondTrust Remote Support Zero-Day Armory Castle SAWFLY BARECLAW

Noticias

CVE-2026-102764: Zero-Day en BeyondTrust Remote Support Explotado por Armory Castle con SAWFLY y BARECLAW

📌Security Roundup Series: Fin de Semana del 19 de Octubre de 2026 • 6 min de lectura deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-102764 (CWE-346 / CWE-290 (Error de Validación de Origen / Evasión de Autenticación por Suplantación)) Severity: CRÍTICA (CVSS 9.3) Threat Actor: Armory Castle (UNC5221 / Warp Panda - Espionaje vinculado

By James Luther