Latest

Daiwa Securities and Scala Communications Supply Chain Cyber Incident

News

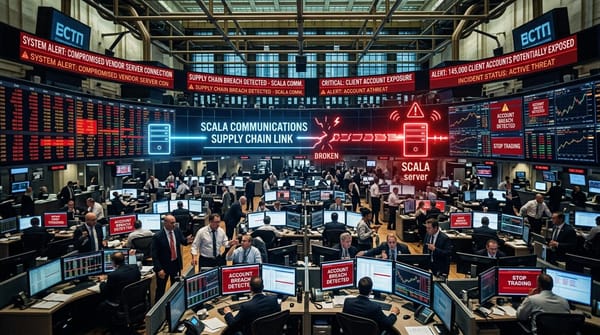
Daiwa Securities Supply Chain Breach: Vendor Server Compromise Exposes 110,000 Client Accounts

📌Security Roundup Series: Weekend of October 5, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Daiwa Securities Group Inc. / Scala Communications Inc. Threat Actor / Attribution: External Threat Actors / Third-Party Vendor Compromise Impact / Records Compromised: 110,000 Wealth Management & Brokerage Client Accounts Initial Attack Vector: Server Infiltration at
By ColibriSec
Monogatari Corporation Yakiniku King Data Leak Tokyo Japan

News

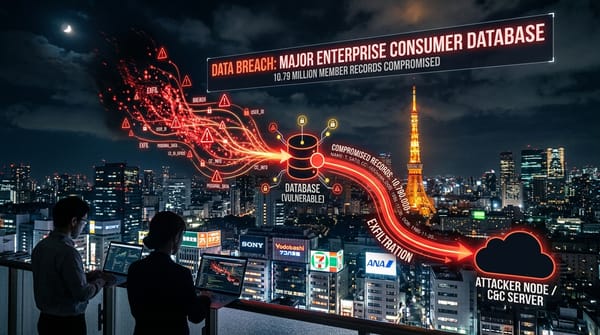
Monogatari Corporation Breach: 10.79 Million Customer Records Leaked in Japanese Hospitality Incident

📌Security Roundup Series: Weekend of October 5, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Monogatari Corporation (Yakiniku King, Marugen Ramen, Syabu-no-Sato) Threat Actor / Attribution: Unattributed Threat Actor / External Cloud Intrusion Impact / Records Compromised: 10,790,000 Customer Member Records Compromised Initial Attack Vector: Unauthorized Ingress into Cloud

By ColibriSec
Denmark National Central Person Register CPR Cyber Breach

News

Denmark Central Person Register Breach: 8.8 Million Citizen Records Exposed via Authorized Partner Misuse

📌Security Roundup Series: Weekend of October 5, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Kingdom of Denmark: Det Centrale Personregister (CPR) Threat Actor / Attribution: Unattributed Threat Syndicate / Compromised Private Partner Access Impact / Records Compromised: 8.8 Million Citizen Records (Current Residents, Expatriates & Historical Records) Initial Attack

By ColibriSec
ColibriSec Weekend Security Roundup October 5 2026

News

Security Roundup: Citrix NetScaler SAML Zero-Day, Denmark 8.8M Registry Breach, Rejetto AI RCE, Asian Financial Infiltrations (Weekend of October 5, 2026)

Executive Summary: The weekend of October 3–5, 2026, delivered an unprecedented surge of critical perimeter exploits, monumental government and enterprise data leaks, and AI-driven intrusion vectors. Headlining the emergency alerts, Citrix confirmed active targeted exploitation of CVE-2026-88779—a high-severity memory overflow zero-day in NetScaler ADC and Gateway configured as

By ColibriSec
Bitget $387.5M Cryptocurrency Exchange Hot Wallet Breach

News

Bitget $387.5M Security Breach: Third-Party Zero-Day and Hot Wallet Risk Analysis

📌Security Roundup Series: Week of October 2, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Bitget Global Cryptocurrency Exchange Threat Actor / Attribution: Suspected State-Sponsored Syndicate (Lazarus Group / DPRK) Impact / Records Compromised: $387.5 Million in Digital Assets (ETH, XRP, USDT, USDC across 11 Blockchains) Initial Attack Vector: Zero-Day

By James Luther
Operation KillSwitch KillSec Ransomware Takedown

News

Operation KillSwitch: Global Takedown of KillSec Ransomware and 110TB Data Seizure

📌Security Roundup Series: Week of October 2, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: KillSec Ransomware-as-a-Service (RaaS) Syndicate Threat Actor / Attribution: Joint International Operation: German LKA, Europol, Eurojust, FBI, UK NCA Impact / Records Compromised: 110 Terabytes of Stolen Enterprise Data Recovered; 5 Infrastructure Nodes Seized Initial Attack

By James Luther
Autonomous Agentic AI Zammad Exploit Chain Analysis

News

DIVD Breach Analysis: Autonomous Agentic AI Exploits Dual Zammad Zero-Days

📌Security Roundup Series: Week of October 2, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Dutch Institute for Vulnerability Disclosure (DIVD) Threat Actor / Attribution: Autonomous Agentic AI Adversary (Unattributed APT / Automated Botnet) Impact / Records Compromised: Compromised Internal Zammad Helpdesk & Volunteer Email Identifiers Initial Attack Vector: Multi-Stage Autonomous

By James Luther