Latest

Guía de Defensa para CISOs 6 de Noviembre de 2026 Xen XSA-523 Alpine OpenSSH sshhole LXD mTLS cPGuard y Cadena de Frío OT

Guía de Defensa para CISOs del 6 de Noviembre de 2026: Blindaje de Xen Dom0, OpenSSH musl en Alpine, LXD mTLS, Paneles cPGuard/CWP, Controladores OT de Cadena de Frío y AD CS

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 9 min de lectura deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-119977, CVE-2026-107441, XSA-523, CVE-2026-112816, CVE-2026-123158 y CVE-2026-58868 (Grant Copy en Hipervisor, Validación mTLS, Retorno de Error en musl crypt(a.plerdy.com), TOCTOU y Control de Acceso OT) Severity: MANUAL

By James Luther
Campaña Poisoned Source de APT29 en Plerdy, Kali365 y VoidProxy PhaaS, Teams AD CS y Brechas en Queens Library Myriad y mSecure

Campaña "Poisoned Source" de APT29 (Plerdy), PhaaS con Señuelos de IA (Kali365 y VoidProxy), Toma de Control AD CS vía Teams y Brechas Globales (Queens Library, Myriad Genetics, mSecure y Japón)

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 9 min de lectura deep dive🏛️Incident Overview: Target / Organization: Sitios con Plerdy SEO (APT29), Empresas M365/Google (Kali365/VoidProxy), Queens Public Library, Myriad Genetics y mSecure Threat Actor / Attribution: APT29 (Midnight Blizzard), Operadores PhaaS Kali365 / VoidProxy, Brain Cipher Ransomware

By James Luther
Ciberataques OT a 50C contra Refrigeración de Supermercados en 7 Países Europeos Danfoss Dixell y Alerta FBI CISA

Sabotaje OT a la Cadena de Frío Europea: Anatomía de los Ciberataques a 50°C contra Refrigeradores de Supermercados en 7 Países y la Alerta Conjunta de FBI y CISA

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 7 min de lectura deep dive🏛️Incident Overview: Target / Organization: Sistemas de Refrigeración Comercial y Cadena de Frío en 7+ Países Europeos (ICA, Coop, Delhaize, Carrefour) Threat Actor / Attribution: Campaña Coordinada de Sabotaje OT Contra Controladores HVAC/R Expuestos a

By James Luther
Brecha LLMjacking en Northflank PaaS, Secuestro DNS en Polymarket DebugBear e Implante Celular en Trezor Safe 5

Secretos Cloud, Web3 e Interdicción de Hardware: Brecha y "LLMjacking" en Northflank PaaS, Secuestro DNS de $3.9M en Polymarket x DebugBear, Implante Celular en Trezor Safe 5 y 600+ IOCs del FBI

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 8 min de lectura deep dive🏛️Incident Overview: Target / Organization: Northflank PaaS, Polymarket (vía DNS de DebugBear), Trezor Safe 5 (vía CryptoBilis) y Billeteras de Binance (Aviso FBI) Threat Actor / Attribution: Atacantes de LLMjacking Cloud, Secuestradores de Registradores DNS, Actores

By James Luther
OpenAI GPT-6 Cyber 948 Exploits Root en Linux, Brecha Agéntica en Chainalysis, SysGoRAT y Haiou

IA Fronteriza en Ciberseguridad: "GPT-6 Cyber" de OpenAI Sintetiza 948 Exploits Root en el Kernel de Linux, Intrusión Agéntica en Chainalysis, SysGoRAT de Unit 42 y Adware "Haiou" en Codex

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 8 min de lectura deep dive🛡️Vulnerability Intelligence: CVE ID: GPT-6 Cyber (1,724 Bugs en Linux Kernel / 948 Exploits Root), CVE-2026-98432 y Escape P1 en ChatGPT (Corrupción de Memoria / Race UAF (Linux Kernel), Wildcard postMessage (ChatGPT) e Inyección de

By James Luther
Ataque a la Cadena de Suministro de cPGuard CDN, Control Web Panel CWPdoor y Launcher PC de NIKKE

Puertas Traseras en la Cadena de Suministro de Hosting y Gaming: Compromiso del CDN de cPGuard en 3,000 Servidores Linux, Implante "CWPdoor" en Control Web Panel y Hackeo del Launcher PC de NIKKE

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 8 min de lectura deep dive🏛️Incident Overview: Target / Organization: OpsShield cPGuard (cPanel/DirectAdmin), Control Web Panel (CWP) y Goddess of Victory: NIKKE (Shift Up / Level Infinite) Threat Actor / Attribution: Grupos de Intrusión en Cadenas de Suministro Contra CDNs de

By James Luther
Boletín de Seguridad de Android Noviembre 2026 CVE-2026-58868 FrameDecoder RCE y CVE-2026-58882 SMS de la Muerte

Boletín de Seguridad de Android de Noviembre 2026: RCE Zero-Click en FrameDecoder.cpp (CVE-2026-58868), UAF en libpng (CVE-2026-58936) y el "SMS de la Muerte" WAP Push de 8 Bytes (CVE-2026-58882)

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 7 min de lectura deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-58868, CVE-2026-58876, CVE-2026-58936 y CVE-2026-58882 (CWE-787 Escritura Fuera de Límites (FrameDecoder.cpp), CWE-416 Use-After-Free (libpng) y CWE-190 Desbordamiento de Enteros (WAP Push)) Severity: CRÍTICA (EJECUCIÓN REMOTA DE CÓDIGO ZERO-CLICK Y

By James Luther
OpenSSH musl libc sshhole CVE-2026-123158 en Alpine Linux y Trampa System Ruby en GitLab CVE-2026-97229

Trampas de Autenticación y Regex en Linux: Análisis de "sshhole" en OpenSSH con musl libc (CVE-2026-123158) sobre Alpine Linux y la Trampa de System Ruby Onigmo en GitLab (CVE-2026-97229)

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 8 min de lectura deep dive🛡️Vulnerability Intelligence: CVE ID: CVE-2026-123158 ("sshhole") y CVE-2026-97229 (GitLab Onigmo) (CWE-287 Autenticación Impropia (OpenSSH/musl) y CWE-190 Desbordamiento de Enteros (Onigmo)) Severity: CRÍTICA / ALTA (EVASIÓN DE AUTENTICACIÓN SSH Y RCE EN CI/

By James Luther
Xen Hypervisor XSA-523 CVE-2026-102703 Escape Dom0 y Canonical LXD CVE-2026-112816 Evasión mTLS

Fugas en Hipervisores y Clústeres Cloud: Escape hacia Dom0 en Xen Hallado por Claude (XSA-523 / CVE-2026-102703 y 102704) y Evasión mTLS CVSS 10.0 en Canonical LXD (CVE-2026-112816)

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 8 min de lectura deep dive🛡️Vulnerability Intelligence: CVE ID: XSA-523 (CVE-2026-102703 y CVE-2026-102704) y CVE-2026-112816 (Confusión de Caché en Grant Copy (Xen) y CWE-295 Validación Impropia de Certificados (LXD)) Severity: CRÍTICA (COMPROMISO TOTAL DEL HIPERVISOR DOM0 Y CLÚSTER ROOT)

By James Luther
WordPress CVE-2026-119977 CISA KEV, Cadena Ivanti Connect Secure y Zyxel GS1900 CVE-2026-107441

Directivas CISA KEV y Zero-Days Perimetrales: Condición de Carrera RCE en WordPress Core (CVE-2026-119977), Cadena Root de 3 Fallos en Ivanti ICS y Evasión de Parche en Switches Zyxel GS1900 (CVE-2026-107441)

📌Security Roundup Series: Semana del 6 de Noviembre de 2026 • 8 min de lectura deep dive🛡️Vulnerability Intelligence: CVE ID: CVE-2026-119977, CVE-2026-104935 / 118527 / 111357 y CVE-2026-107441 (CWE-367 (Condición de Carrera TOCTOU), CWE-340 / CWE-306 y CWE-787 (Escritura Fuera de Límites)) Severity: CRÍTICA (EXPLOTACIÓN ACTIVA EN LA RED Y MANDATOS CISA KEV)

By James Luther
CISO Defense Blueprint Black October Finale Kernel MPTCP Fragnesia IDE Extensions EIP-7702 and ESXi

News

CISO Defense Blueprint for the "Black October" Finale: Kernel MPTCP/Fragnesia Shields, IDE Extension Governance, ESXi Audit Heartbeats & EIP-7702 Custody Controls

📌Security Roundup Series: Week of October 30, 2026 • 8 min read deep dive🏛️Incident Overview: Target / Organization: Enterprise Defense-in-Depth Architecture Blueprint (Week of October 30, 2026) Threat Actor / Attribution: Countering AI-Synthesized Kernel Exploits, RCE-to-Root KEV Chains, IDE Extension Trojans, Hypervisor Log Blinding & EIP-7702 Custody Drains Impact / Records Compromised: Actionable

By James Luther
SilentRansomGroup Susman Godfrey LLP Qilin Ransomware Proterial and Rhysida Extortion Wave

News

Corporate & Legal Extortion Wave: SilentRansomGroup Targets Susman Godfrey LLP, Qilin Hits Proterial (Hitachi Metals) & Rhysida Academic Breaches

📌Security Roundup Series: Week of October 30, 2026 • 7 min read deep dive🏛️Incident Overview: Target / Organization: Susman Godfrey LLP (U.S. Litigation Law Firm), Proterial, Ltd. (Japan, formerly Hitachi Metals) & INTI International University Threat Actor / Attribution: SilentRansomGroup / Luna Moth (Susman Godfrey), Qilin RaaS (Proterial) & Rhysida / N0n (Academic

By James Luther
UNM Health System Byod Cyberattack Federal Election Commission 41-Hour Outage and Ohio Auditor Intrusion

News

U.S. Public Sector & Healthcare Cyber Crisis: UNM Health Level-I Trauma Diversion ("Byod"), FEC 41-Hour Pre-Midterm Outage & Ohio Auditor Intrusion

📌Security Roundup Series: Week of October 30, 2026 • 7 min read deep dive🏛️Incident Overview: Target / Organization: University of New Mexico Health System (UNM Health), U.S. Federal Election Commission (FEC), Ohio Auditor of State & Barbour County Schools (WV) Threat Actor / Attribution: Extortion Syndicate "Byod" (UNM Health

By James Luther
Microsoft .NET Out-of-Band Brotli CVE-2026-111497 Drupal Commerce CVE-2026-118539 and Oracle EBS CVE-2026-101767

News

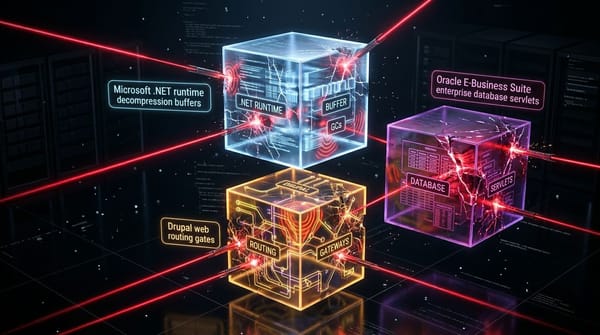
Enterprise Stack Under Siege: Microsoft .NET Out-of-Band Brotli Patch (CVE-2026-111497), Drupal Commerce Core Auth Bypass (CVE-2026-118539) & Oracle EBS SQLi (CVE-2026-101767)

📌Security Roundup Series: Week of October 30, 2026 • 7 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-111497 (.NET OOB), CVE-2026-118539 (Drupal) & CVE-2026-101767 (Oracle EBS) (CWE-787 (Out-of-Bounds Write), CWE-862 (Missing Authorization) & CWE-89 (SQL Injection)) Severity: CRITICAL (OUT-OF-BAND PATCH & ACTIVE WILD EXPLOITATION) (CVSS 9.8 (Brotli & Oracle

By James Luther
Binance 6.36 Billion Heist TraderTraitor and Ethereum Pectra EIP-7702 Smart Contract Delegation

News

Anatomy of the $6.36 Billion Binance Multi-Chain Heist: How TraderTraitor Weaponized Ethereum Pectra EIP-7702 Pre-Signed Nonce Tuples

📌Security Roundup Series: Week of October 30, 2026 • 8 min read deep dive🏛️Incident Overview: Target / Organization: Binance Hot Wallet Infrastructure (10 Blockchains Including Ethereum, BSC, Tron & Arbitrum) Threat Actor / Attribution: TraderTraitor / Lazarus Group (DPRK State-Sponsored Cyber Unit — Attributed by TRM Labs & Chainalysis) Impact / Records Compromised: $6.36

By James Luther
Cursor Marketplace Supply Chain Compromise Trojanized Claude Code v2.1.313 SSH Backdoor

News

Cursor Marketplace Supply-Chain Compromise: Dissecting the Trojanized Claude Code v2.1.313 Extension, svc-telemetry SSH Key & 134.209.82.225 C2

📌Security Roundup Series: Week of October 30, 2026 • 7 min read deep dive🏛️Incident Overview: Target / Organization: Cursor IDE Extension Marketplace / Open-VSX Registry (anthropic.claude-code v2.1.313) Threat Actor / Attribution: Unattributed Supply-Chain Threat Actor (C2 Infrastructure: 134.209.82.225:8099) Impact / Records Compromised: Up to 5,000 Cursor

By James Luther
CVE-2026-98432 Linux Kernel TCP MPTCP Race Use-After-Free and Claude AI Root Exploit

News

CVE-2026-98432 (CVSS 9.8): Inside the Linux Kernel TCP/MPTCP Race Use-After-Free & How Claude Synthesized a Remote Root Exploit in Under 60 Minutes

📌Security Roundup Series: Week of October 30, 2026 • 8 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-98432 (CWE-416 (Use After Free) & CWE-362 (Concurrent Execution Race Condition)) Severity: CRITICAL (REMOTE KERNEL USE-AFTER-FREE RCE) (CVSS 9.8) Threat Actor: Demonstrated by Anthropic Frontier Red-Team (Claude Autonomous Synthesis in <60

By James Luther
Cisco ASA FTD CVE-2026-76418 GitLab CVE-2026-97229 and VMware ESXi Warp Panda CVE-2026-41709 CISA KEV

News

CISA KEV Zero-Day Directives: Cisco ASA/FTD SSL VPN DoS (CVE-2026-76418), GitLab CVSS 10.0 RCE (CVE-2026-97229) & VMware ESXi "Warp Panda" Log Suppression (CVE-2026-41709)

📌Security Roundup Series: Week of October 30, 2026 • 8 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-76418, CVE-2026-97229 & CVE-2026-41709 (CWE-690 (NULL Pointer Deref), CWE-190 (Integer Overflow) & CWE-778 (Insufficient Logging)) Severity: CRITICAL (CISA KEV ZERO-DAY & RCE DIRECTIVES) (CVSS 8.6 (Cisco), 10.0 (GitLab) & 2.7

By James Luther
PHP2Shell CVE-2026-109618 and Linux Kernel Fragnesia CVE-2026-46300 CISA KEV Root Exploit Chain

News

Weaponized in the Wild: How Threat Actors Chain PHP2Shell (CVE-2026-109618/19) with Linux Kernel "Fragnesia" (CVE-2026-46300) for Root Takeover

📌Security Roundup Series: Week of October 30, 2026 • 8 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-109618, CVE-2026-109619 & CVE-2026-46300 (CWE-416 (Use After Free) & CWE-665 / Page-Cache Shared Fragment Corruption) Severity: CRITICAL (ACTIVE CISA KEV RCE-TO-ROOT CHAIN) (CVSS 9.2 (PHP2Shell) & 7.8 (Fragnesia)) Threat Actor: China-Nexus Intrusion

By James Luther
ColibriSec Weekly Security Roundup October 30 2026 - Black October Finale Matrix

News

Security Roundup: PHP2Shell + Fragnesia Kernel Chains, Cisco & GitLab KEV Zero-Days, Linux MPTCP UAF, Cursor Claude Code Backdoor & $6.36B Binance EIP-7702 Heist (Week of October 30, 2026)

Executive Summary: The final week of October 2026 (October 24–30, 2026) has cemented "Black October" as the most volatile month in modern cybersecurity history. Over the past seven days, threat actors bridged the gap between AI-discovered runtime bugs and kernel-level infrastructure takeovers, chaining the pre-authentication PHP2Shell vulnerabilities

By James Luther
Black October Enterprise Hardening Blueprint Polyglot Runtimes ESXi VMDK and AI Sandboxes

guides

Enterprise Hardening Blueprint for "Black October": Polyglot Runtime Guards, Python .pth Integrity, ESXi VMDK Protection & AI Sandbox Zero-Egress

📌Security Roundup Series: Weekend of October 26, 2026 • 8 min read deep dive🛡️Vulnerability Intelligence: CVE ID: DEFENSE-IN-DEPTH ARCHITECTURAL BLUEPRINT (Runtime Memory Safety, Supply-Chain Integrity, Hypervisor Isolation & AI Containment) Severity: STRATEGIC & ENGINEERING PLAYBOOK (CVSS N/A) Threat Actor: Countering AI-Discovered Zero-Days, Supply-Chain RATs, ESXi Ransomware & Autonomous Agent

By James Luther
SafePay AA26-293A Emperador Ransomware AB InBev Capcom ID 11.77M and PingCAP TiDB Cloud Breaches

News

Ransomware & Mega-Breach Forensics: CISA SafePay Advisory (AA26-293A), Emperador Hits AB InBev, Capcom ID (11.77M) & PingCAP TiDB Cloud

📌Security Roundup Series: Weekend of October 26, 2026 • 7 min read deep dive🏛️Incident Overview: Target / Organization: Global Enterprise & Consumer Targets: SafePay (600+ Orgs), AB InBev, Capcom ID (11.77M), PingCAP TiDB Cloud, CenterPoint Energy (7.49M) & Burger King Japan (11.18M) Threat Actor / Attribution: SafePay Closed-Group Operation

By James Luther